THORChain Review: What Changed After the Vault Exploit?

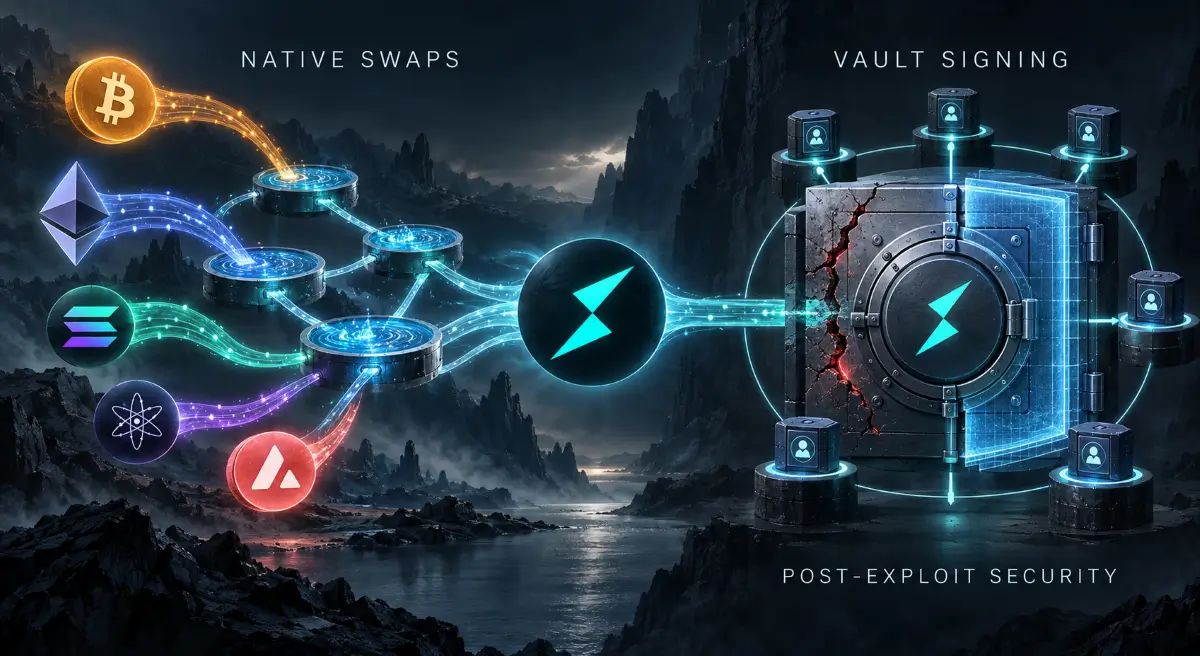
THORChain native swaps contrasted with vault signing and post-exploit security risk

THORChain’s May 2026 vault exploit did not begin in its swap logic. A malicious validator exploited three weaknesses in the GG20 threshold-signing implementation and eventually reconstructed one Asgard vault key. This THORChain Review looks at what changed after that failure: signer hardening, solvency controls, validator churn, RUNE supply, and the dependencies that still matter. Trading returned in June. v3.20 later restored validator churn, followed by v3.20.1 on 27 August. The documented exploit path has been patched, but GG20 still appears in THORChain’s production vault-signing architecture for relevant ECDSA paths. Recovery is measurable. The signer remains the core security test. Native Swaps Move Trust Into Vault Signing THORChain coordinates liquidity across independent blockchains so users can exchange supported native assets without relying on wrapped versions. A BTC-to-ETH swap illustrates the difference. Users send native BTC into a THORChain-controlled inbound vault, the protocol prices and routes the trade, and a validator committee authorizes the outbound asset on the destination chain. That removes dependence on a wrapped-token issuer, but it does not remove trust from the system. During settlement, protocol vaults hold native assets. Validators jointly control spending authority through threshold cryptography, while chain observers, signing software, liquidity pools and emergency controls all sit inside the broader security boundary. This model differs from cross-chain messaging designs, where a protocol may only deliver a message and leave asset control to another application. THORChain directly manages vaults containing native assets. No single honest validator should possess a complete vault key. May’s exploit mattered because the attacker found a way around that assumption. What the May Exploit Actually Broke A malicious node entered the active validator set on 13 May 2026 and joined one of five Asgard vault committees. Over roughly two and a half days, the operator deliberately generated 864 failed GG20 signing rounds. Repeated failures were not merely operational noise. They created enough interactions to exploit weaknesses in THORChain’s threshold-signing implementation. The attack combined three implementation problems: incomplete validation of Paillier cryptographic material, information leakage during a masking step, and a weak proof condition that allowed invalid inputs through. None was enough on its own. Together, repeated signing attempts leaked small pieces of information about other validators’ key shares. Eventually, the attacker reconstructed the affected vault’s ECDSA private key. Once that happened, the security model changed completely. Destination chains did not see an attacker bypassing THORChain consensus. They saw mathematically valid signatures produced by a valid private key. Approximately $10.7 million left the affected vault. Four other Asgard vaults were not compromised, while signature paths outside the vulnerable GG20 route were not exposed to this specific exploit. THORChain’s technical exploit report documents the interacting weaknesses and subsequent mitigations. Attack stage What happened Why it mattered Post-exploit response Validator entry Malicious operator joined the active set Permissionless participation cannot identify intent Security work focused on signer validation and monitoring Key setup Malformed cryptographic material entered the protocol Existing validation was incomplete Stronger modulus validation and proofs Repeated signing 864 failed rounds were forced Retries leaked useful information Vulnerable proof paths were hardened Key reconstruction One vault key was recovered Threshold approval was no longer required Documented exploit chain was patched Unauthorized outbounds Destination chains accepted valid signatures Detection came after signing authority was lost Solvency controls limited further damage Solvency Controls Contained Damage, but Did Not Prevent the Failure THORChain already compared observed vault balances with the balances its internal accounting expected. Unauthorized withdrawals created a mismatch. Solvency controls detected the divergence and began halting affected routes. Node operators later added manual pauses and governance actions until the network reached a controlled halt. Containment mattered. One vault was compromised rather than all five. Prevention and containment are still different security functions. Once the attacker possessed a reconstructed private key, Bitcoin, Ethereum and other destination chains could not distinguish the malicious signature from an authorized one. Solvency monitoring could identify disappearing assets, but it could not invalidate signatures that had already been accepted. Similar validator-control trade-offs appear elsewhere in crypto. Fast emergency intervention can limit damage, but emergency authority does not remove the weakness that made intervention necessary. What the Patch Fixed – and What It Did Not THORChain first focused on restoring a safe operating path. Version 3.18.1 addressed immediate signer risk, while later releases carried additional recovery and migration work. Trading returned around 22 June after roughly five weeks of disruption. Signer patches strengthened validation around the three weaknesses used in the attack. Breaking any one part of that exploit chain would have prevented the documented key-recovery method, the patched implementation addresses all three. That is meaningful remediation. It is not proof that threshold signing can never fail again. Complex cryptographic software can contain unknown implementation flaws even when its underlying mathematics remains sound. A security patch closes a known path. It does not prove the absence of every future path. Production evidence therefore matters more than a statement that the incident has been fixed. GG20 Still Matters After the Exploit THORChain has not completed a network-wide replacement of GG20. Current THORNode architecture still describes GG20 within vault management for relevant signing paths. Alternative schemes such as DKLS and FROST matter because they can reduce dependence on the cryptographic family involved in May’s incident where appropriate. Development work is not the same as production migration. The accurate post-exploit claim is narrower: THORChain patched the vulnerable GG20 implementation, restarted the network, and continues work on alternative threshold-signature systems. My review gives more weight to whichever signer actually controls production vaults than to a future migration plan. v3.20 Restored Churn, but Recovery Is Still Being Tested The v3.20 tag was published on 19 August, with mainnet activation following later in the month, v3.20.1 was released on 27 August. Restoring validator churn was especially important. THORChain had paused normal rotation during recovery, leaving vault committees and validator participation more static than usual. By THORChain’s 4 September network report, the active set stood at 87 nodes, with 80 more in standby and 83.47 million RUNE bonded, rotation … Read more

SEDA Protocol Review: Custom Data, Hidden Trust Trade-Offs

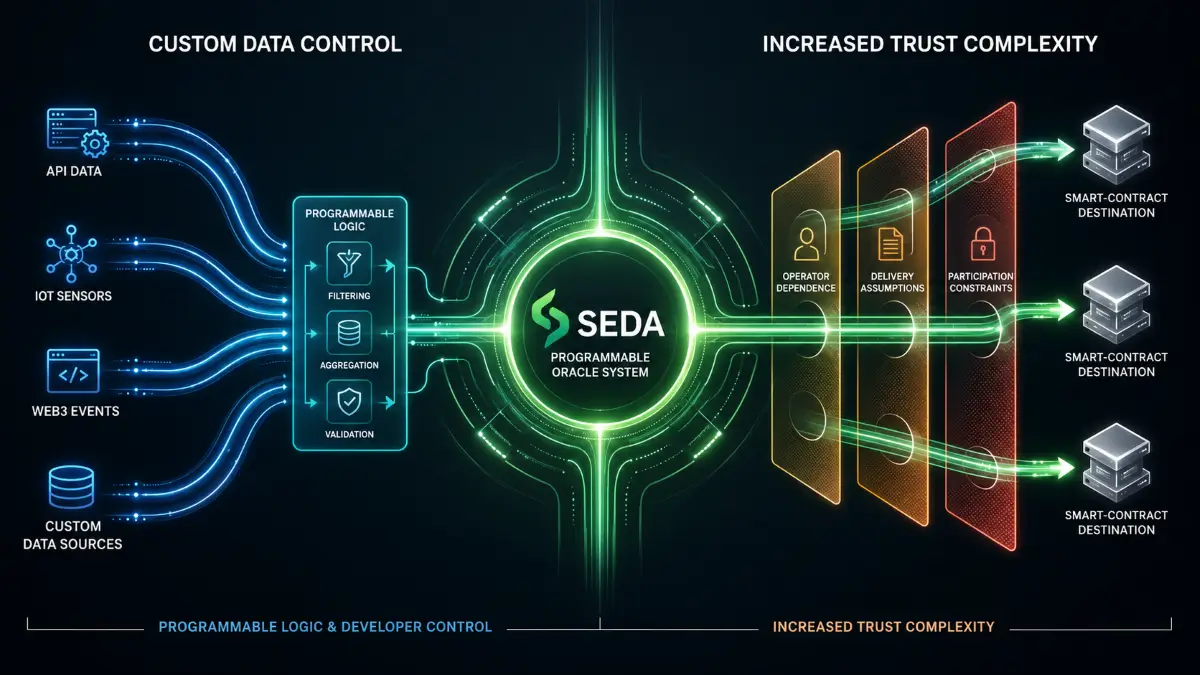
Programmable oracle architecture connecting custom data sources with operator, delivery and participation dependencies

This SEDA Protocol Review examines the unusual freedom SEDA gives developers for an oracle network. They can choose the source, define the calculation, set the replication level, and decide how the result reaches another chain. That flexibility is the product. It is also the risk surface. The review follows each handoff from source to destination. The aim is not to ask whether SEDA can move data. It can. The useful question is whether an application can explain who supplied the data, how SEDA processed it, who relayed the result, and what the receiving contract accepts as valid. SEDA Lets Developers Program the Oracle Itself SEDA is an application-specific Layer 1 for programmable oracle infrastructure. It uses Cosmos SDK and CometBFT for the base chain. Oracle Programs define the instructions used to retrieve, filter, aggregate, calculate, and return external data. That is different from asking a network for one predefined market feed. A builder can request public API data, use private data through a proxy, combine several sources, or apply custom logic before the result reaches an application. The Oracle Program documentation describes these programs as WASM-based instructions that tell the network what to query and how to process the response. The flexibility can support markets that do not fit a standard feed. It can also move more responsibility toward the builder. A well-secured network cannot make a weak source reliable. It cannot fix a bad weighting rule. It cannot reject an economically strange answer unless the Oracle Program or receiving application defines that rule. One Data Request Crosses Several Trust Boundaries A SEDA data request does not travel through one component. A Solver can relay the request to SEDA. Overlay Nodes query the sources named by the Oracle Program. The tally phase applies the program’s calculation rules. Validators coordinate the chain state and sign data batches. A Solver then returns the result to a destination-side Prover Contract, where an application can consume it. Each step solves a different problem. Layer Main job Main question SEDA Chain Consensus, batching and canonical state How distributed is validator control? Oracle Program Source selection and computation Are the rules appropriate and inspectable? Overlay Network External data retrieval Who operates the nodes, and how many sources are queried? Solver Network Request and result relay Can delivery fail, stall, or become concentrated? Prover Contract Destination verification Which signer, proof and upgrade rules apply? Receiving application Final acceptance decision What happens when data is stale, missing, or implausible? Oracle security is not one signature. It is a chain of decisions. That same distinction appears in our cross-chain verification analysis. A result can be authentic while the system around it still contains weak assumptions. Source Quality Remains Outside Consensus External data creates a problem that blockchains cannot solve through consensus alone. If ten nodes read the same incorrect API, consensus can faithfully agree on the wrong answer. SEDA gives Oracle Programs tools to reduce that risk. Builders can select several sources. They can choose a replication factor. Overlay Nodes can query independently and commit results before revealing them. Those controls help only when the configuration uses them well. A program that depends on one exchange still inherits that exchange’s outage risk. Poor weighting can still distort a multi-source result. Private providers can still publish bad values. Developers should be able to explain their endpoints, missing-data rules, outlier handling, and fallback logic. Customization is valuable when those rules are clear. It becomes another trust layer when they are not. The comparison with a more standardized oracle model is useful here. A fixed or established feed can reduce configuration freedom. SEDA moves in the opposite direction and gives builders more control over the feed itself. Neither approach removes the need to inspect the exact feed. The Overlay Network Has Its Own Decentralization Question SEDA’s base chain and its Overlay Network should not receive one shared decentralization label. The chain uses proof of stake. Validators produce blocks and participate in batch signing. The MiCA material describes an active validator set capped at up to 100, selected by delegated stake. The Overlay Network performs a different job. Its nodes fetch the external data requested by Oracle Programs. SEDA documentation describes the long-term Overlay model as permissionless.It also says the rollout occurs in phases, with phase one using an allowlisted group of professional validator companies. A staged rollout can explain both statements. Secret committees and commit-reveal can reduce some coordination risks. They do not prove that operators have independent ownership, infrastructure, or incentives. The useful measurements are operator count, stake concentration, committee diversity, and the process for adding or removing participants. Solvers Move Results, but They Do Not Make Results True The Solver Network connects SEDA with destination chains. Solvers watch for requests, quote the cost of relaying them, submit requests to SEDA, and return completed results to Prover Contracts. The model lets independent Solver operators compete. A requestor can settle with a Solver in a currency that the Solver accepts. The Solver still needs SEDA inventory to pay the network-side execution costs. That detail matters for token analysis later. It also matters for reliability. A Solver outage can interrupt delivery without changing the truth of the underlying data. A destination contract can also contain its own verification or upgrade risk. Our interoperability risk review makes the same distinction. Transport security and source truth are separate problems. A valid proof of delivery does not prove that the original API was accurate. SEDA FAST Changes Latency, Not the Meaning of Trust SEDA FAST provides a lower-latency delivery path for Oracle Programs. SEDA’s delivery documentation says endpoint latency can be as fast as 50 milliseconds in internal benchmarks. That is not an end-to-end guarantee. Readers should not convert speed into a broader security claim. A fast response can still come from a weak source. A signed response can still contain a calculation that the receiving application should reject. Network latency also differs from the total time between a real-world event, source publication, data retrieval, … Read more