Peaq Network Review: Can Machines Create PEAQ Demand?
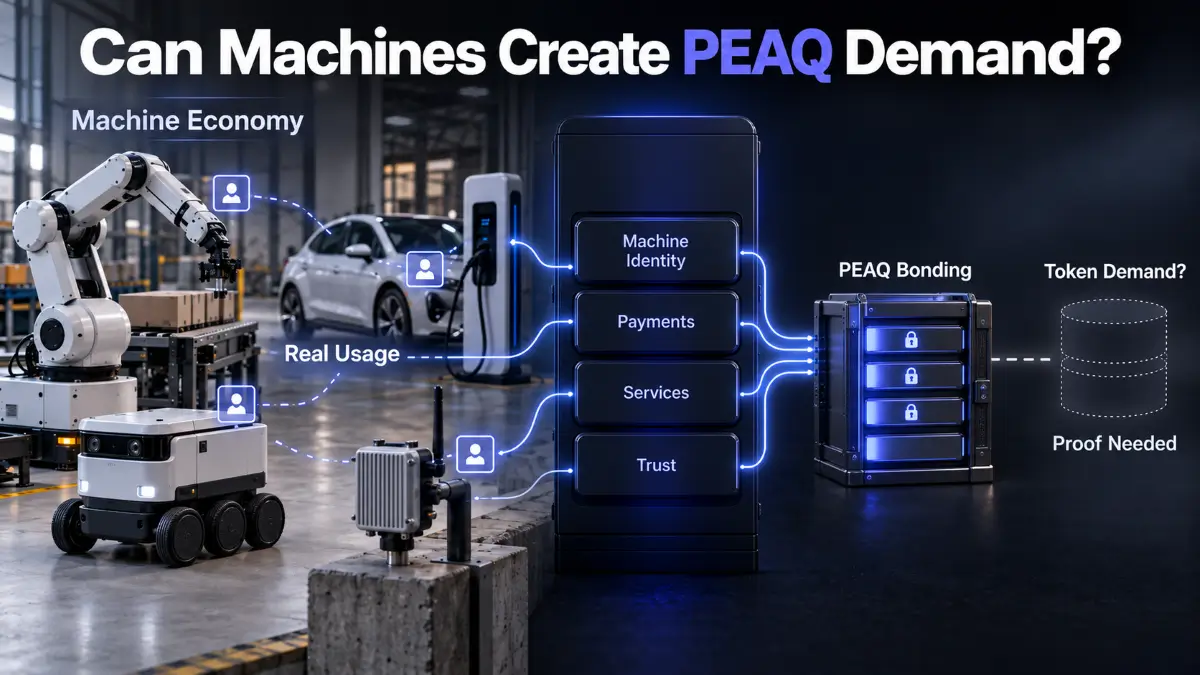
Peaq has live machine infrastructure and a clearer trust-layer thesis, but PEAQ still needs proof that machine growth can outpace unlocks and issuance.

Evidence-led cryptocurrency reviews examining protocol design, token supply, governance, security evidence, adoption claims and material risks. Facts, project claims and editorial analysis are separated, with primary sources used where available. Content does not provide buy or sell recommendations.
Peaq has live machine infrastructure and a clearer trust-layer thesis, but PEAQ still needs proof that machine growth can outpace unlocks and issuance.
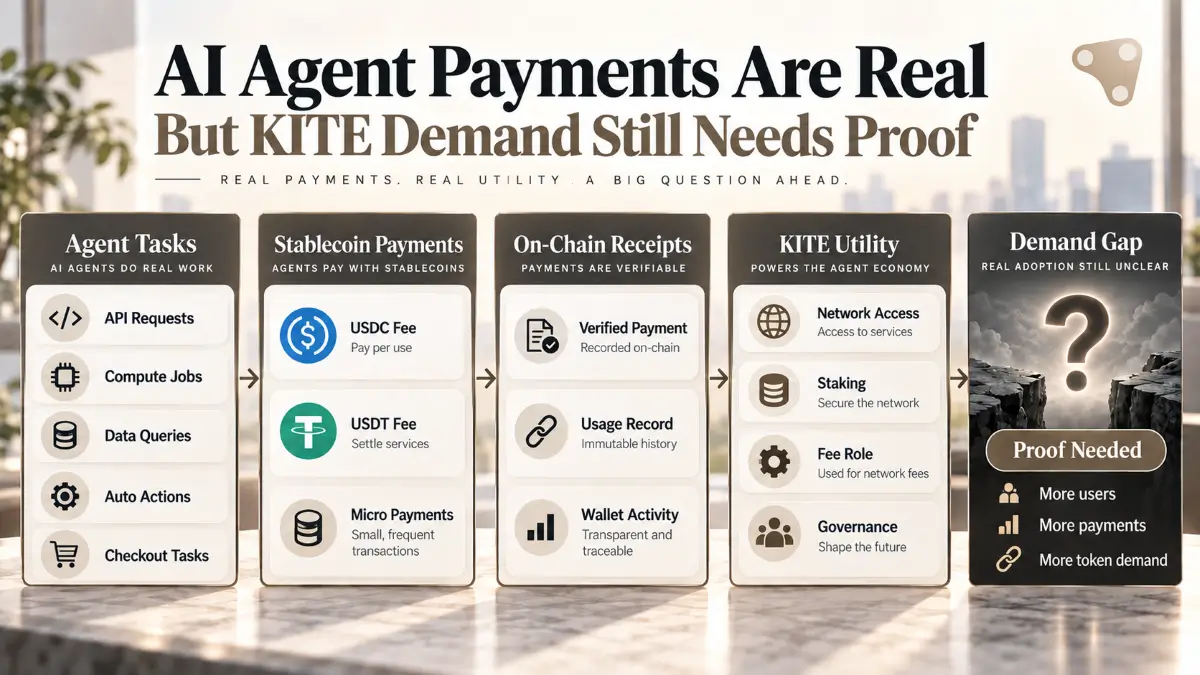
Kite has a strong agent-payments story, but KITE still needs proof that real usage creates durable token demand.
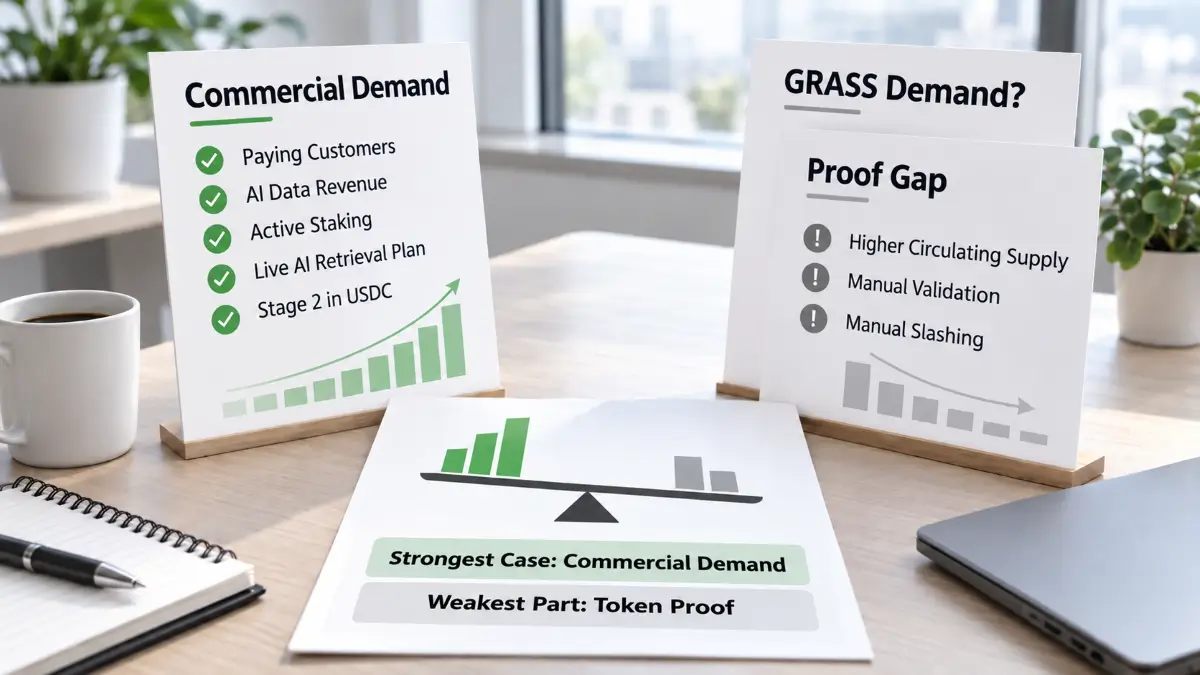
Grass now reports real AI data revenue, but GRASS still needs clearer proof that customer payments create durable token demand.
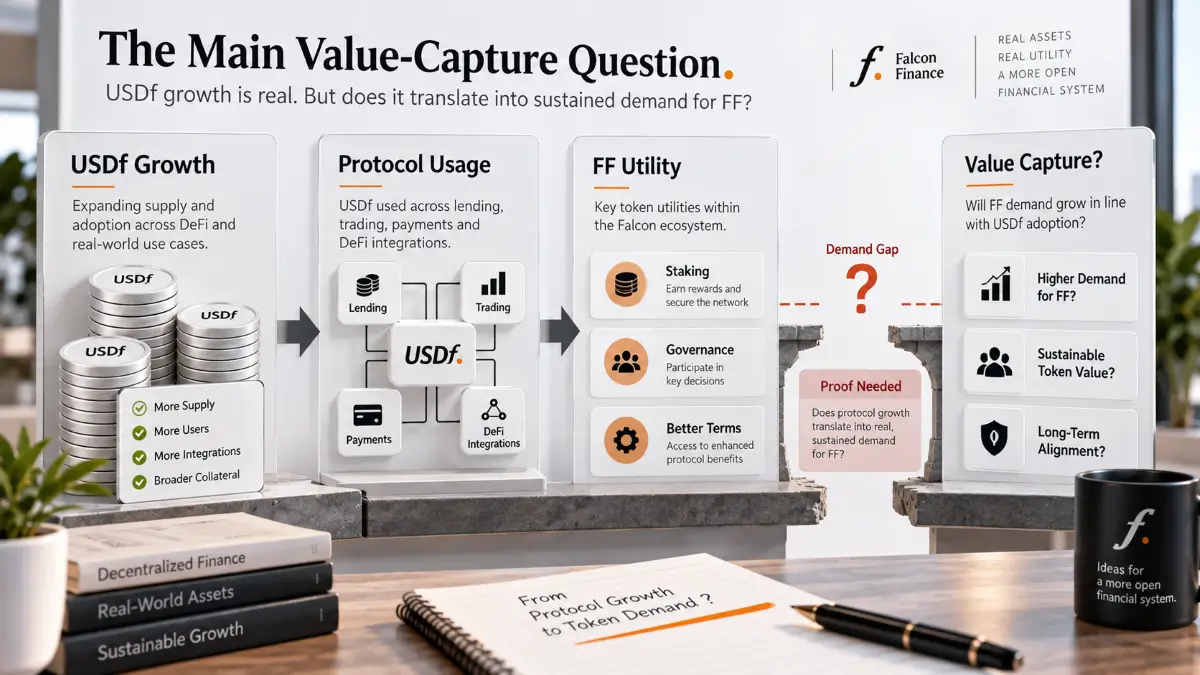
Falcon Finance has strong USDf growth and a serious RWA narrative, but FF still needs clearer proof that protocol usage creates durable token demand.
MarsCoin links taxable trading activity to SPCXB rewards, but exchange volume, audit gaps and tokenized-security risks keep value capture uncertain.
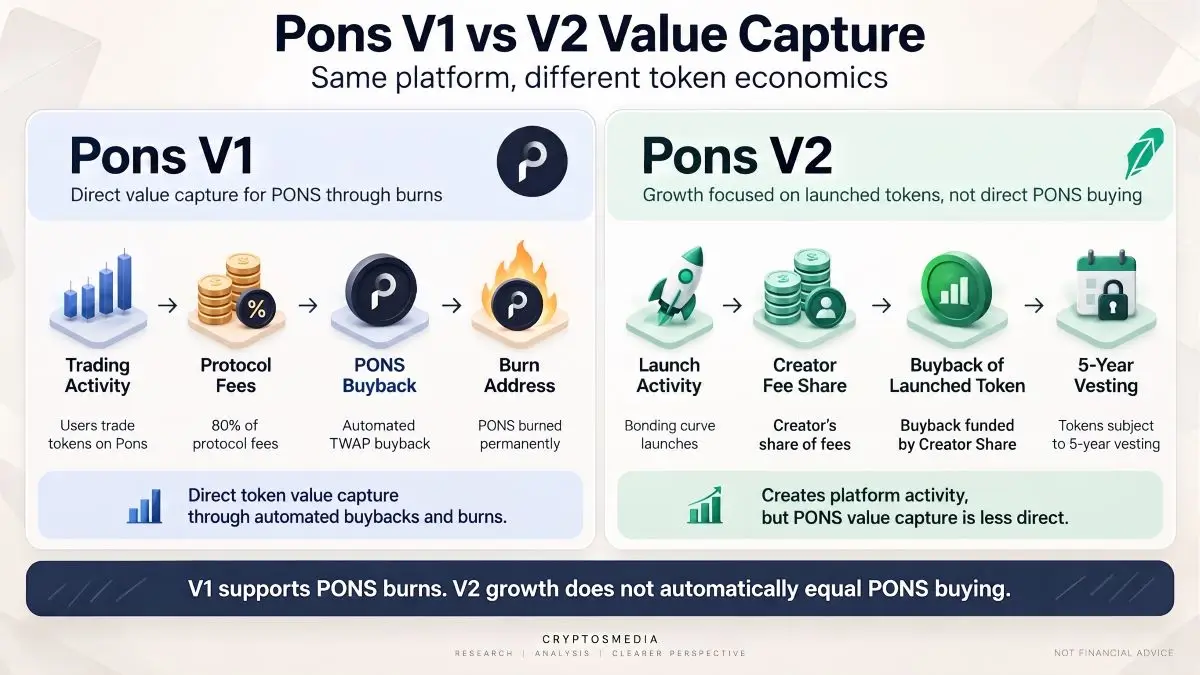
Pons has proved real launchpad activity and fee generation, but v2 growth does not automatically create direct demand for PONS.
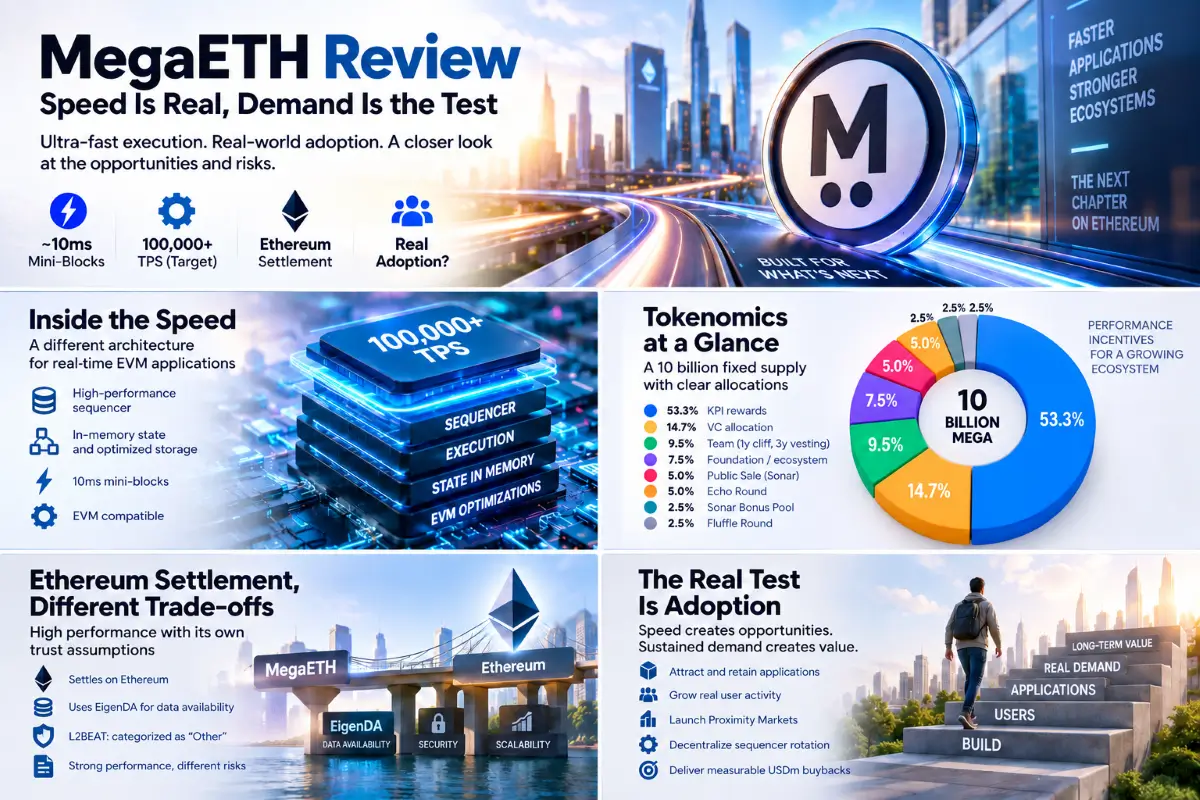
MegaETH delivers unusually fast Ethereum-based execution, but token utility, sequencer decentralization and ecosystem retention are still being proved.
THORChain’s May 2026 vault exploit did not begin in its swap logic. A malicious validator exploited three weaknesses in the GG20 threshold-signing implementation and eventually reconstructed one Asgard vault key. This THORChain Review looks at what changed after that failure: signer hardening, solvency controls, validator churn, RUNE supply, and the dependencies that still matter. Trading returned in June. v3.20 later restored validator churn, followed by v3.20.1 on 27 August. The documented exploit path has been patched, but GG20 still appears in THORChain’s production vault-signing architecture for relevant ECDSA paths. Recovery is measurable. The signer remains the core security test. Native Swaps Move Trust Into Vault Signing THORChain coordinates liquidity across independent blockchains so users can exchange supported native assets without relying on wrapped versions. A BTC-to-ETH swap illustrates the difference. Users send native BTC into a THORChain-controlled inbound vault, the protocol prices and routes the trade, and a validator committee authorizes the outbound asset on the destination chain. That removes dependence on a wrapped-token issuer, but it does not remove trust from the system. During settlement, protocol vaults hold native assets. Validators jointly control spending authority through threshold cryptography, while chain observers, signing software, liquidity pools and emergency controls all sit inside the broader security boundary. This model differs from cross-chain messaging designs, where a protocol may only deliver a message and leave asset control to another application. THORChain directly manages vaults containing native assets. No single honest validator should possess a complete vault key. May’s exploit mattered because the attacker found a way around that assumption. What the May Exploit Actually Broke A malicious node entered the active validator set on 13 May 2026 and joined one of five Asgard vault committees. Over roughly two and a half days, the operator deliberately generated 864 failed GG20 signing rounds. Repeated failures were not merely operational noise. They created enough interactions to exploit weaknesses in THORChain’s threshold-signing implementation. The attack combined three implementation problems: incomplete validation of Paillier cryptographic material, information leakage during a masking step, and a weak proof condition that allowed invalid inputs through. None was enough on its own. Together, repeated signing attempts leaked small pieces of information about other validators’ key shares. Eventually, the attacker reconstructed the affected vault’s ECDSA private key. Once that happened, the security model changed completely. Destination chains did not see an attacker bypassing THORChain consensus. They saw mathematically valid signatures produced by a valid private key. Approximately $10.7 million left the affected vault. Four other Asgard vaults were not compromised, while signature paths outside the vulnerable GG20 route were not exposed to this specific exploit. THORChain’s technical exploit report documents the interacting weaknesses and subsequent mitigations. Attack stage What happened Why it mattered Post-exploit response Validator entry Malicious operator joined the active set Permissionless participation cannot identify intent Security work focused on signer validation and monitoring Key setup Malformed cryptographic material entered the protocol Existing validation was incomplete Stronger modulus validation and proofs Repeated signing 864 failed rounds were forced Retries leaked useful information Vulnerable proof paths were hardened Key reconstruction One vault key was recovered Threshold approval was no longer required Documented exploit chain was patched Unauthorized outbounds Destination chains accepted valid signatures Detection came after signing authority was lost Solvency controls limited further damage Solvency Controls Contained Damage, but Did Not Prevent the Failure THORChain already compared observed vault balances with the balances its internal accounting expected. Unauthorized withdrawals created a mismatch. Solvency controls detected the divergence and began halting affected routes. Node operators later added manual pauses and governance actions until the network reached a controlled halt. Containment mattered. One vault was compromised rather than all five. Prevention and containment are still different security functions. Once the attacker possessed a reconstructed private key, Bitcoin, Ethereum and other destination chains could not distinguish the malicious signature from an authorized one. Solvency monitoring could identify disappearing assets, but it could not invalidate signatures that had already been accepted. Similar validator-control trade-offs appear elsewhere in crypto. Fast emergency intervention can limit damage, but emergency authority does not remove the weakness that made intervention necessary. What the Patch Fixed – and What It Did Not THORChain first focused on restoring a safe operating path. Version 3.18.1 addressed immediate signer risk, while later releases carried additional recovery and migration work. Trading returned around 22 June after roughly five weeks of disruption. Signer patches strengthened validation around the three weaknesses used in the attack. Breaking any one part of that exploit chain would have prevented the documented key-recovery method, the patched implementation addresses all three. That is meaningful remediation. It is not proof that threshold signing can never fail again. Complex cryptographic software can contain unknown implementation flaws even when its underlying mathematics remains sound. A security patch closes a known path. It does not prove the absence of every future path. Production evidence therefore matters more than a statement that the incident has been fixed. GG20 Still Matters After the Exploit THORChain has not completed a network-wide replacement of GG20. Current THORNode architecture still describes GG20 within vault management for relevant signing paths. Alternative schemes such as DKLS and FROST matter because they can reduce dependence on the cryptographic family involved in May’s incident where appropriate. Development work is not the same as production migration. The accurate post-exploit claim is narrower: THORChain patched the vulnerable GG20 implementation, restarted the network, and continues work on alternative threshold-signature systems. My review gives more weight to whichever signer actually controls production vaults than to a future migration plan. v3.20 Restored Churn, but Recovery Is Still Being Tested The v3.20 tag was published on 19 August, with mainnet activation following later in the month, v3.20.1 was released on 27 August. Restoring validator churn was especially important. THORChain had paused normal rotation during recovery, leaving vault committees and validator participation more static than usual. By THORChain’s 4 September network report, the active set stood at 87 nodes, with 80 more in standby and 83.47 million RUNE bonded, rotation … Read more
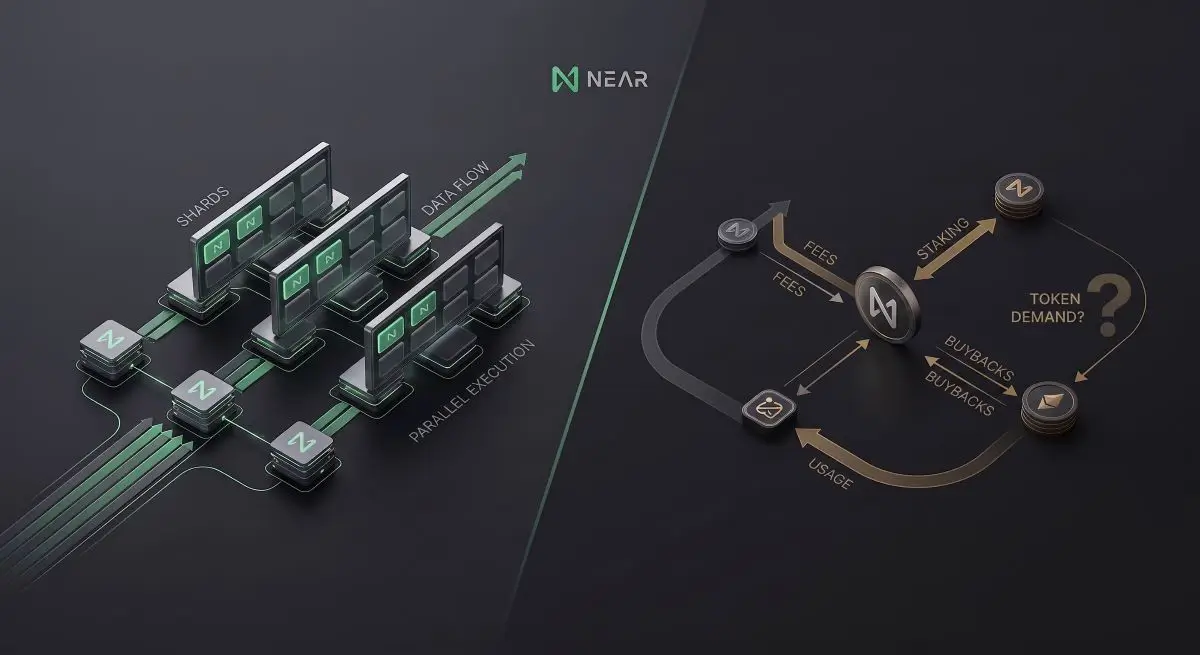
My review focused on two separate questions: can Nightshade scale NEAR effectively, and can that extra capacity create durable demand for the NEAR token? Those questions are related, but they are not the same. NEAR now combines sharded execution with Intents, MPC-based Chain Signatures and confidential infrastructure. Each layer removes friction somewhere in the user journey, while also adding dependencies beyond ordinary Layer 1 consensus. What stood out during review was the gap between technical capacity and economic capture. NEAR has credible evidence that its architecture can process more work. Turning that capability into recurring fees, retained revenue and sustained token demand remains a separate test. What NEAR Actually Does NEAR is a proof-of-stake Layer 1 where validators produce blocks, verify shard-specific chunks and stake NEAR as economic collateral. Nightshade handles scaling by dividing state and execution across shards. Work no longer needs to pass through one execution lane, yet those shards remain coordinated inside the same base protocol. Stateless validation reduces how much state validators need to retain. Chunk producers provide state witnesses containing the information required to verify transitions, shifting more of the verification process toward witness production and checking. Dynamic resharding adds another layer of flexibility. NEAR can split or merge shards as network demand changes instead of depending only on fixed partitions. NEAR’s current architecture describes nine shards, 600 millisecond blocks and about 1.2 second finality. A modular data-availability design such as Celestia separates more of the execution, settlement and data-publication stack. NEAR keeps public sharded execution within one coordinated base layer. For users, that can create a more unified environment. For validators and developers, cross-shard receipts, state movement and resharding still need to work reliably when traffic changes. One Million TPS Shows Headroom, Not Everyday Demand NEAR reported a benchmark above one million transactions per second across 70 shards. Native-token transfers were used for the test, a lighter workload than many DeFi transactions, smart-contract interactions or multichain routes. My reading of the result is narrow: Nightshade can scale a defined workload horizontally when more shards are added. It does not mean current mainnet sustains one million transactions every second. Mainnet uses far fewer shards, while real applications create very different workloads. A benchmark can prove technical headroom without proving that users will fill the available capacity. From a token-demand perspective, retained activity matters more than headline TPS. Spare capacity creates little economic value unless users return, applications generate fees and those fees eventually feed into NEAR’s economic model. Chain Signatures Move Complexity Behind the Interface Chain Signatures allow a NEAR account or smart contract to authorize transactions on external networks through multi-party computation. Current NEAR documentation describes an eight-node MPC service. No single node can sign alone, threshold consensus is required. Such a setup can remove several wallet, gas-token and bridge-management steps from the user experience. One application may coordinate actions that previously required separate wallets and manual transfers. Convenience, however, widens the dependency map. MPC operators, threshold rules, software availability and destination-chain security remain part of the transaction path. NEAR consensus cannot repair an outage on Bitcoin, reverse a faulty external contract or guarantee that every connected chain remains available. A cross-chain model such as LayerZero provides a useful comparison. Supporting more networks does not automatically make interoperability safer. Verification paths, upgrade authority and failure recovery matter more than integration count alone. Intents Create a Measurable Revenue Channel NEAR Intents use an outcome-based model. Users specify what they want to receive, while solvers compete to find and execute a route. A verifier contract on NEAR checks settlement. Intents can remove much of the routing, bridge selection and gas-token management from the user’s side. Solver competition may also improve execution when enough liquidity is available. External markets, solver behaviour, liquidity and destination-chain conditions still determine whether a route works as expected. A cleaner interface does not remove those dependencies. My 3 September 2026 check of NEAR’s revenue dashboard showed about $3.85 million in gross fees and $1.00 million in net revenue over the previous 30 days. Net revenue carried more weight in this review than routed volume because transaction size does not show how much value NEAR actually retains after payouts. NEAR’s dashboard also tracks a dedicated buyback wallet. Those purchases create a measurable demand channel, but they should not automatically count as a burn. Permanent supply reduction only occurs if repurchased NEAR is irreversibly removed from circulation. Validator Participation Is Broad, but Stake Still Clusters NEAR uses several validator roles, allowing some operators to produce blocks and chunks while others perform narrower validation duties. A 1 September 2026 NearBlocks snapshot showed 423 active validator entries, about 624.2 million NEAR staked and total supply near 1.305 billion NEAR. Seat price stood close to 10,000 NEAR. Validator metric 1 Sep 2026 snapshot Why it matters Active validator entries 423 Broad participation at account level Total staked 624.2M NEAR About 47.8% of total supply Total supply 1.305B NEAR Context for staking and issuance Seat price About 10,000 NEAR Entry changes with network conditions Last-epoch APY About 5.2% Staker yield differs from supply-wide issuance Top-eight cumulative stake About 33.5% Material concentration among largest entries 423 active validator entries suggest broad participation, but the stake distribution changes that picture. In the snapshot, the eight largest validator entries together held roughly one-third of active stake. That figure does not prove common ownership, coordination or malicious behaviour. It does show why validator count alone gives an incomplete picture of decentralization. A similar issue appears in networks with validator concentration trade-offs. Beneficial ownership, delegation flows, shared infrastructure and cumulative voting weight can matter more than the number of names shown in an explorer. NEAR Tokenomics: Issuance Still Matters NEAR started with one billion coins at genesis. Current total supply has grown above 1.3 billion, with no verified fixed maximum under the current monetary model. Validator rewards now target 2.5% of total supply annually. Older material often repeats the former 5% figure, which no longer reflects the current target. Legacy token allocations … Read more
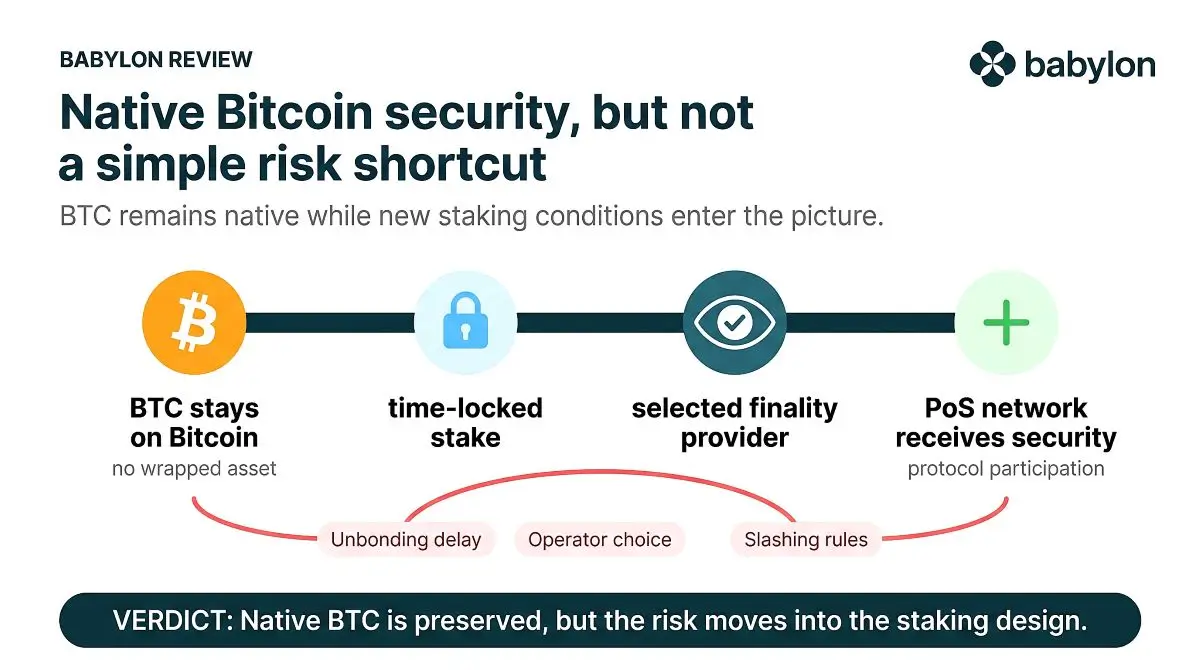
Evidence-led review of Babylon’s Bitcoin-staking architecture, BABY utility, validator model, airdrop distribution, slashing assumptions, and staking risks.